Manage your CA hierarchy
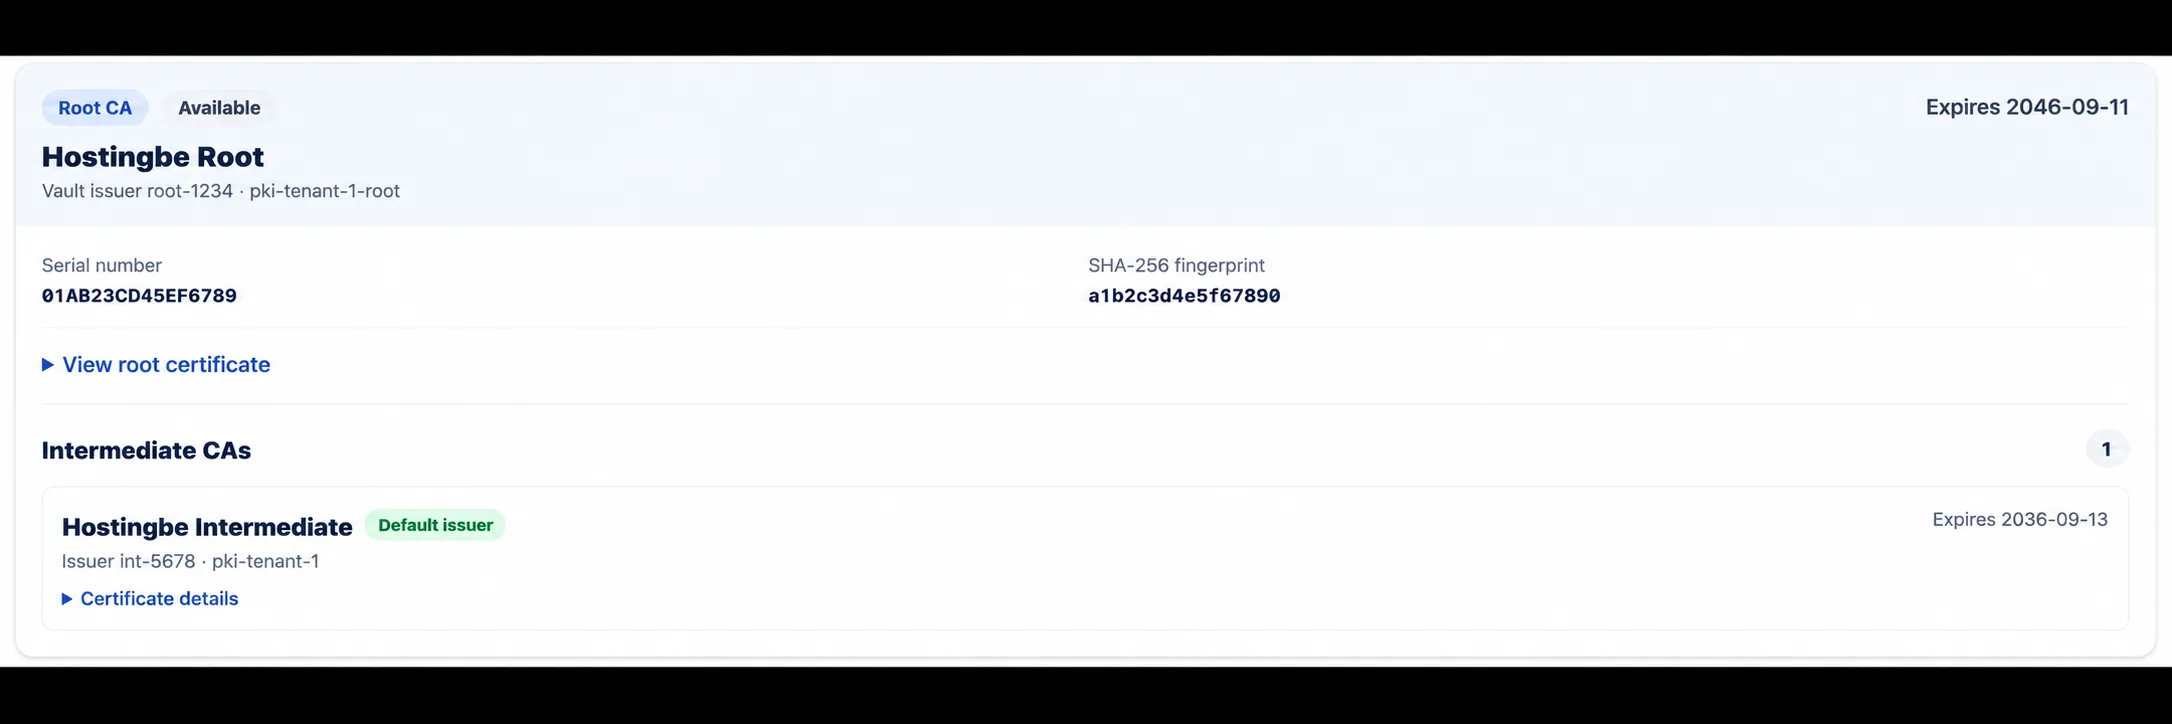
Keep root and intermediate certificate authorities organized, with a clear view of who issues your certificates.
From your first root CA to hundreds of internal certificates. Issue, organize and monitor your private PKI in one clear workspace.
Start with 1 root CA, 1 intermediate and 10 active internal certificates. Free.
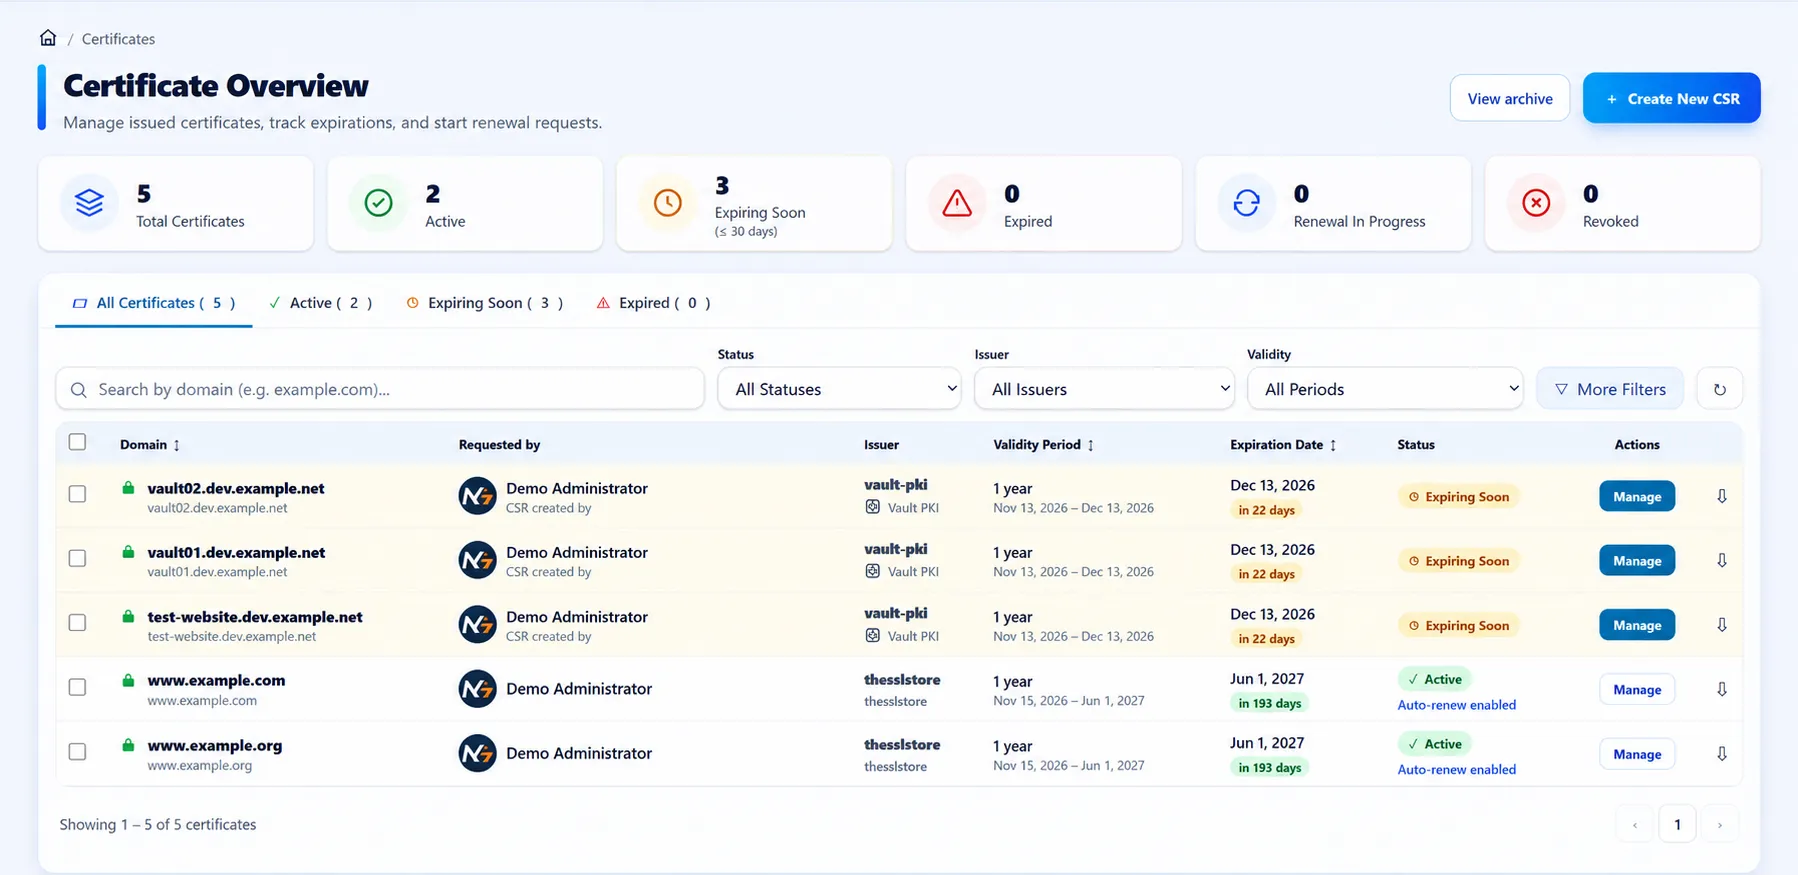
Internal services need certificates too. Give your team one place to manage certificate authorities, follow certificate lifecycles and see what needs attention.
Keep root and intermediate certificate authorities organized, with a clear view of who issues your certificates.
Review internal certificates, their status and expiry dates without maintaining another spreadsheet.
Use expiry reminders and certificate visibility to plan renewals before services are affected.
Issue certificates for your allowed internal domains using the appropriate intermediate CA.
Keep organizations separate and give users access that matches their role and responsibilities.
Review certificate activity and see who requested a certificate when the requester is known.
Create root and intermediate certificate authorities, or bring your existing hierarchy into your workspace. Keep the relationships visible as your environment grows.
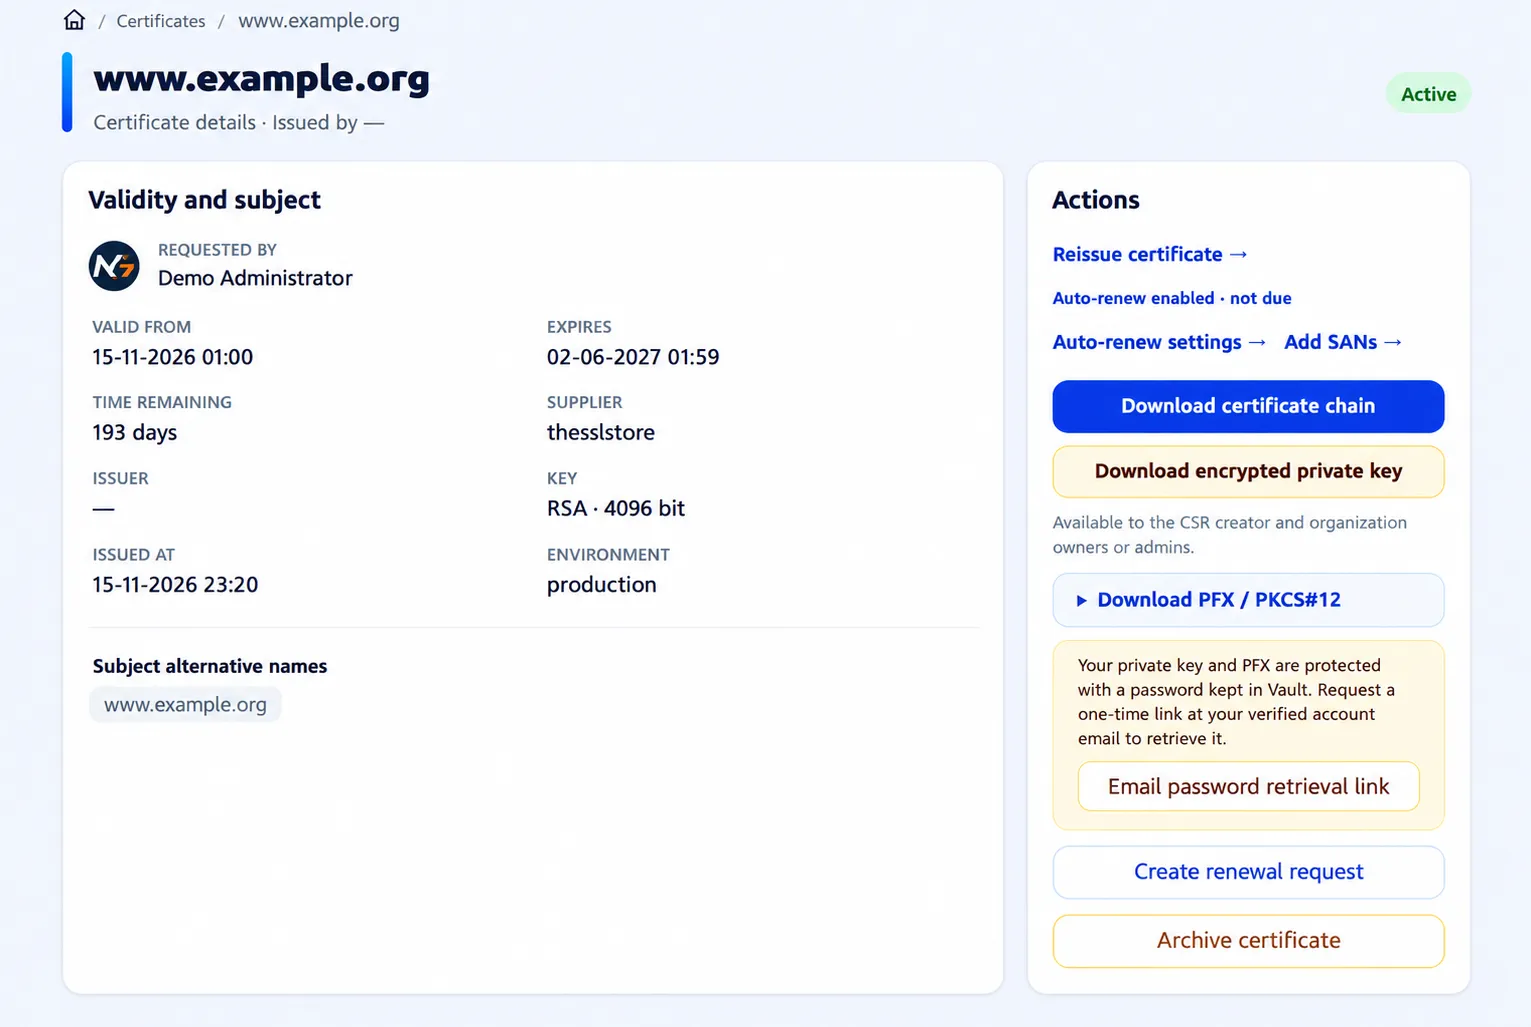
Find the certificate you need, check its issuer and expiry date, and manage its next step without digging through spreadsheets.
Start small, establish trust and manage your certificates as a team.
Create or import your root and intermediate CAs. Define which internal domains your organization can issue certificates for.
Request certificates for your internal services. Install them on the relevant systems and distribute your root certificate to devices that need to trust it.
Track expiry dates, use reminders and review certificate activity. Renew certificates before they expire and revoke them when needed.
HashiCorp Vault handles the certificate authority keys. Certificate Manager gives your team the interface to manage issuance, visibility and day-to-day work.
Choose the capacity your organization needs. Package limits apply to active internal certificates and certificate authorities per organization.
For your first internal services.
For teams managing a growing PKI.
For larger internal environments.
Paid plans require an approved business account. Prices exclude VAT; applicable VAT is calculated during billing.
Need more than 500 active certificates? Contact us for a custom package
Questions before you get started? Here are the essentials.
Talk to our teamInternal certificates secure connections to private services such as intranets, internal applications and infrastructure endpoints. Your organization controls the certificate authority and which devices trust it.
No. Certificates from your private CA are trusted only by devices and applications configured to trust your root certificate. Distribute that root certificate through your device management or other approved trust configuration.
Yes. You can import an existing root certificate and an intermediate certificate with its private key into the Vault-backed PKI setup, or create a new hierarchy. Plan the migration and trust distribution before switching your services.
The Free package includes 1 root CA, 1 intermediate CA and up to 10 active internal certificates per organization, with certificate management through the app. Upgrade when you need more capacity.
No. These packages cover internal PKI management. Publicly trusted SSL certificates are ordered and billed separately.
Use the app to renew internal certificates and deploy the renewed certificate to your service. Expiry visibility and reminders help you plan this work; deployment to your endpoints remains part of your own operational workflow.
Start with a free workspace and make your internal certificates easier to manage, monitor and maintain.
We accept payments via