
What Is an Intermediate Certificate Authority and How Do You Create One?
Introduction
An Intermediate Certificate Authority (Intermediate CA) acts as the link between a trusted Root Certificate Authority (Root CA) and certificates issued for websites, servers, applications, and devices. This hierarchy is an essential part of Public Key Infrastructure (PKI).
The Problem: Issuing Certificates Directly from the Root CA
The Root CA serves as the trust anchor of a PKI. If its private key is compromised, the entire certificate hierarchy may be affected.
For this reason, the Root CA’s private key is typically protected by strict security controls and preferably kept offline.
Using the Root CA for everyday certificate issuance would unnecessarily expose this critical component. A separate certificate authority layer provides a more secure and manageable approach.
The Solution: An Intermediate CA
An Intermediate CA receives a CA certificate signed by a higher-level Certificate Authority.
Using its corresponding private key, the Intermediate CA can issue end-entity certificates within the restrictions defined by its certificate and applicable policies.
This allows organizations to issue certificates without involving the Root CA in every operation.
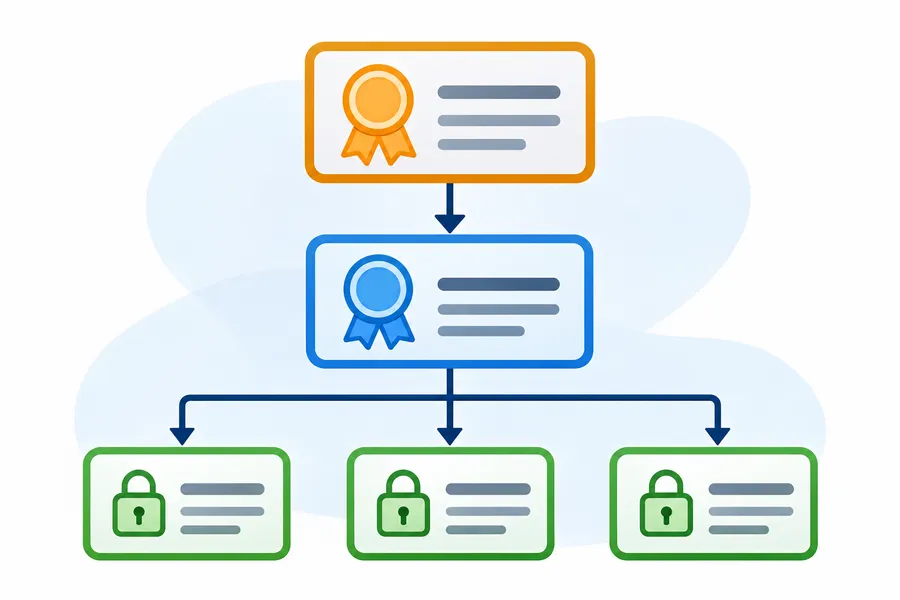
A typical certificate hierarchy looks like this:
Root CA
  └── Intermediate CA
        ├── www.example.com
        ├── api.example.com
        └── mail.example.com
When establishing a TLS connection, a client validates the certificate chain back to a trusted root certificate.
This validation includes checking digital signatures, certificate validity periods, permitted certificate usage, and, where applicable, certificate revocation status.
Differences Between a Root CA and an Intermediate CA
Although both Root and Intermediate Certificate Authorities are part of the same PKI hierarchy, they have different responsibilities.
| Component | Root CA | Intermediate CA |
|---|---|---|
| Role | Trust anchor | Issues subordinate certificates |
| Signature | Typically self-signed | Signed by a higher-level CA |
| Private Key | Preferably kept offline and strictly protected | Protected within a controlled CA environment |
| Trust | Explicitly trusted by the client or organization | Derived from a trusted certificate chain |
Benefits and Common Use Cases
An Intermediate CA helps organizations separate responsibilities, reduce the operational exposure of the Root CA, and manage certificate issuance across multiple environments.
Common use cases include:
- Internal servers: Issuing certificates for internal websites, APIs, and infrastructure services.
- VPN infrastructure: Securing VPN gateways and authenticating connected devices.
- Device identities: Providing certificates for network devices, servers, and IoT equipment.
- Client authentication: Authenticating users and devices using client certificates.
- Environment separation: Managing independent certificate policies for production, testing, and development.
- Government and enterprise infrastructure: Centralizing certificate management across municipalities, provinces, and larger organizations.
An Intermediate CA also makes it easier to separate certificate issuance responsibilities between departments or infrastructure teams.
However, an Intermediate CA does not eliminate security risks.
If an Intermediate CA is compromised, revocation may be necessary. This can also affect every certificate issued by that CA.
The primary security benefit is that the Root CA remains protected from routine certificate issuance operations.
Creating an Intermediate CA Using Certificate Manager
Important: The following Control Panel instructions describe a proposed workflow. Verify that your Certificate Manager environment supports requesting or signing Intermediate CA certificates.
A standard SSL certificate order does not grant permission to issue certificates independently.
Step 1: Sign In to Certificate Manager
Sign in to the Certificate Manager Control Panel using your account credentials.
Step 2: Open Certificate Authorities
Navigate to Certificate Authorities or Intermediate CA, if this functionality is available for your account.
Step 3: Start a New Intermediate CA Request
Select Create Intermediate CA or Request Intermediate CA.
Step 4: Enter Your Organization Details
Provide the required information, such as:
- Organization name.
- Desired Intermediate CA name.
- Country and organizational details.
- Contact information.
- Additional information required by the issuing Certificate Authority.
Step 5: Generate a Certificate Signing Request
Generate a new private key and Certificate Signing Request (CSR) in a secure environment.
The CSR contains the public key and identifying information required to request the Intermediate CA certificate.
Keep the private key under your control and never share it with third parties.
Only submit the CSR to the issuing Certificate Authority.
For production environments, using a Hardware Security Module (HSM) or an equivalent secure key management solution is strongly recommended.
Step 6: Submit the Request
Submit the CSR to a higher-level Certificate Authority that is explicitly authorized and willing to issue Intermediate CA certificates.
Complete any required validation and security checks.
The exact requirements depend on the issuing CA and whether the Intermediate CA will operate within a private or publicly trusted PKI.
Step 7: Install the Intermediate CA Certificate
After approval, the issuing CA provides the signed Intermediate CA certificate.
Import this certificate and its associated certificate chain into your PKI environment.
Make sure the certificate matches the private key generated during the CSR creation process.
Step 8: Configure Certificate Issuance
Before issuing end-entity certificates, configure the required security and operational controls.
These should include:
- Certificate issuance policies.
- Access permissions and administrative roles.
- Certificate logging and auditing.
- Certificate revocation mechanisms.
- Certificate expiration monitoring.
- Backup and recovery procedures.
Screenshot placeholder: Certificate Manager Control Panel — Certificate Authorities overview showing the Create Intermediate CA action, if supported.
Publicly Trusted vs. Private Intermediate CAs
Creating an Intermediate CA under a publicly trusted Root CA is significantly different from operating a private Intermediate CA.
Publicly trusted Certificate Authorities must comply with strict industry requirements and generally do not offer Intermediate CA certificates as standard SSL products.
For internal PKI environments, organizations may operate their own Root CA and issue Intermediate CA certificates beneath it.
However, a private Root CA must be explicitly trusted by the clients and systems that use certificates issued within that hierarchy.
Verifying an Intermediate CA Certificate with OpenSSL
After receiving an Intermediate CA certificate, you can inspect its properties using OpenSSL.
Run the following command:
openssl x509 -in intermediate-ca.pem -noout -textA typical Intermediate CA certificate may contain extensions similar to these:
X509v3 Basic Constraints: critical
    CA:TRUE, pathlen:0

X509v3 Key Usage: critical
    Certificate Sign, CRL Sign
The CA:TRUE setting indicates that the certificate is intended to function as a Certificate Authority.
The pathlen:0 constraint generally prevents the issuance of additional non-self-issued subordinate CA certificates beneath this Intermediate CA.
However, the Intermediate CA may still issue end-entity certificates if permitted by its remaining certificate extensions and applicable policies.
The exact certificate extensions depend on the issuing CA and its certificate policies.
Verify the Certificate Chain
You can verify the Intermediate CA certificate against its trusted Root CA using:
openssl verify -CAfile root-ca.pem intermediate-ca.pemExample of a successful verification:
intermediate-ca.pem: OKA successful result indicates that OpenSSL was able to validate the certificate against the supplied trust anchor under the applicable verification rules.
Security Risks and Management Considerations
Operating an Intermediate CA introduces additional security and operational responsibilities.
Because an Intermediate CA can issue certificates, its private key is a particularly sensitive security asset.
A compromised private key could allow an attacker to issue unauthorized certificates within the scope of that CA.
Organizations should implement appropriate security measures, including:
- Private key protection: Preferably store the private key in a Hardware Security Module (HSM).
- Access control: Restrict certificate issuance permissions to authorized administrators and services.
- Audit logging: Maintain detailed records of certificate issuance and administrative activities.
- Certificate revocation: Implement Certificate Revocation Lists (CRLs) or Online Certificate Status Protocol (OCSP) services where applicable.
- Expiration monitoring: Monitor the validity periods of CA certificates and issued certificates.
- Backup and recovery: Maintain secure backup and disaster recovery procedures.
- Certificate policy enforcement: Ensure issued certificates comply with the organization’s security requirements.
Incorrect configuration of an Intermediate CA can affect many systems simultaneously.
Regular security reviews and monitoring are therefore essential for maintaining a reliable PKI environment.
Conclusion
An Intermediate Certificate Authority provides a secure and scalable approach to certificate issuance without requiring the Root CA to participate in daily operations.
For organizations managing large numbers of servers, applications, and devices, Intermediate CAs offer improved operational flexibility, clearer separation of responsibilities, and more manageable certificate hierarchies.
Municipalities, provinces, and enterprise organizations can particularly benefit from a well-structured PKI with dedicated Intermediate CAs for different environments or services.
Creating an Intermediate CA through Certificate Manager is possible only when the Control Panel and the selected issuing Certificate Authority support this functionality.
With appropriate security controls and certificate management procedures, an Intermediate CA provides a solid foundation for reliable certificate issuance and long-term PKI management.